Case study · Team project
InspireHub
Students submit project ideas, and admins approve or reject them. I set up the project and built its Express and MongoDB API, as one of four people, in a week.
- My role
- Project setup and the API: Express, MongoDB, sign-in
- Team
- 4, with Abdulaziz Alhazmi (opens in a new tab), Rana Almalki (opens in a new tab) and Najwa Almutairi
- Timeline
- Oct 2024, 1 week
- Context
- Tuwaiq Academy · team of 4
- Platform
- React app with an Express API
01 Overview
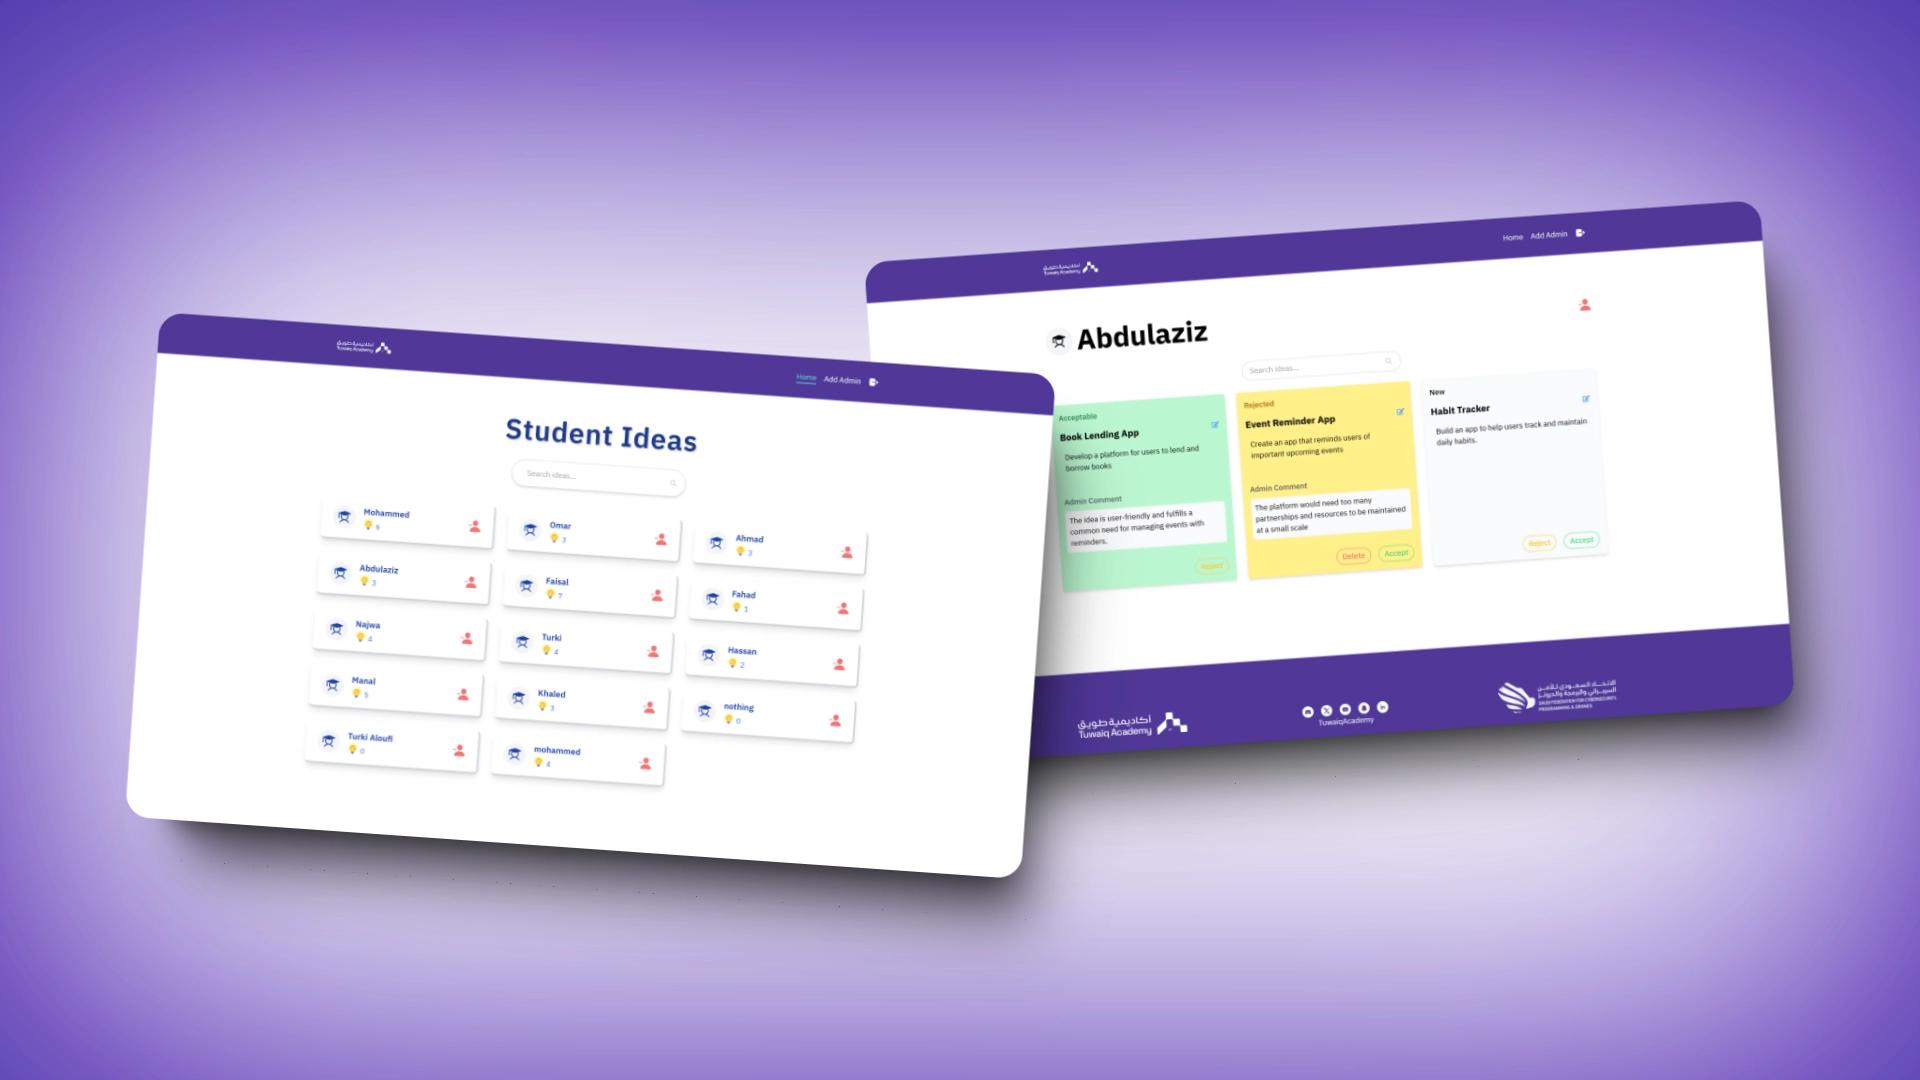
InspireHub is where students submit, edit and save project ideas, and where admins review them: approve or reject with one click, or delete an idea.
- 7 Days
- 4 People
- 2 Roles: student and admin
02 Problem
A class needs one place where students submit ideas and instructors approve them, with the status visible to both.
Constraints
One week from the first commit to delivery, with four people building pages at the same time as the API.03 My role
I set up the project on day one, built the whole API and connected it to the pages.
- SetupCreated the Vite project, the routing and the shared styles
- APIBuilt the Express and MongoDB backend: sign-in with JWT and bcrypt, users, ideas and validators
- IntegrationConnected the student ideas and admin pages to the API
- PagesBuilt parts of the student ideas, admin and home pages
- TeammateAbdulaziz AlhazmiNavbar, footer and admin page (opens in a new tab)
- TeammateRana AlmalkiHome page and idea cards (opens in a new tab)
- TeammateNajwa AlmutairiRegistration page
- Frontend
 React
 Vite
 Tailwind CSS
 React Router
 Axios
 JavaScript
 CSS
 HTML
- Backend
 Node.js
 Express
 MongoDB
 Mongoose
 JSON Web Tokens
- Hosting and tools
 Render
 ESLint
 Git
 GitHub
- Design
 Figma
 Canva
04 Key decisions
The choices that shaped the product. Open one to see why it was made and what it cost.
One sign-in for every role
What we chose
A role on each user, sent with the sign-up form and stored in the JWT
Why
One sign-in flow for students and admins, with the pages switching by role.
Trade-off
The API doesn't check the role on admin routes, so anyone who signs up as an admin is one. A server-side check is the fix.
Tokens in the browser
What we chose
The JWT kept in localStorage and sent as a Bearer header
Why
Quick to wire up in a week.
Trade-off
Any script on the page can read the token; an httpOnly cookie would be safer.
05 Result
Delivered on Oct 17, 2024: students register, then submit, edit and save ideas; admins approve, reject and delete them.
What I learned
Building the API while three teammates built pages taught me to agree on the endpoints first. Next time I'd check roles on the server and keep the token in an httpOnly cookie.
With thanks to
Next project: Blogmors
A responsive blog I designed and built in React, with searchable posts, topic filters and author pages.
Questions